Wikileaks Under Attack

The WikiLeaks website crashed Tuesday in an apparent cyberattack after the accelerated publication of tens of thousands of once-secret State

Destroy Ur Friends PC Using Virus

In this post we'll take a look on how to create a deadly computer virus to destroy your enemy or victim's PC.

USB 3.0 Evolution xD

USB 3.0 > Usb 2.0 > Usb 1.0 xD

MEet Top ten techies Who changed World around Us

Top Ten Techies...

Steal Your Frnds Password using Flash Drive

Yes Ew Heard it Correct...CLick to know the trick :)

Showing posts with label online tech. Show all posts

Saturday, 24 August 2013

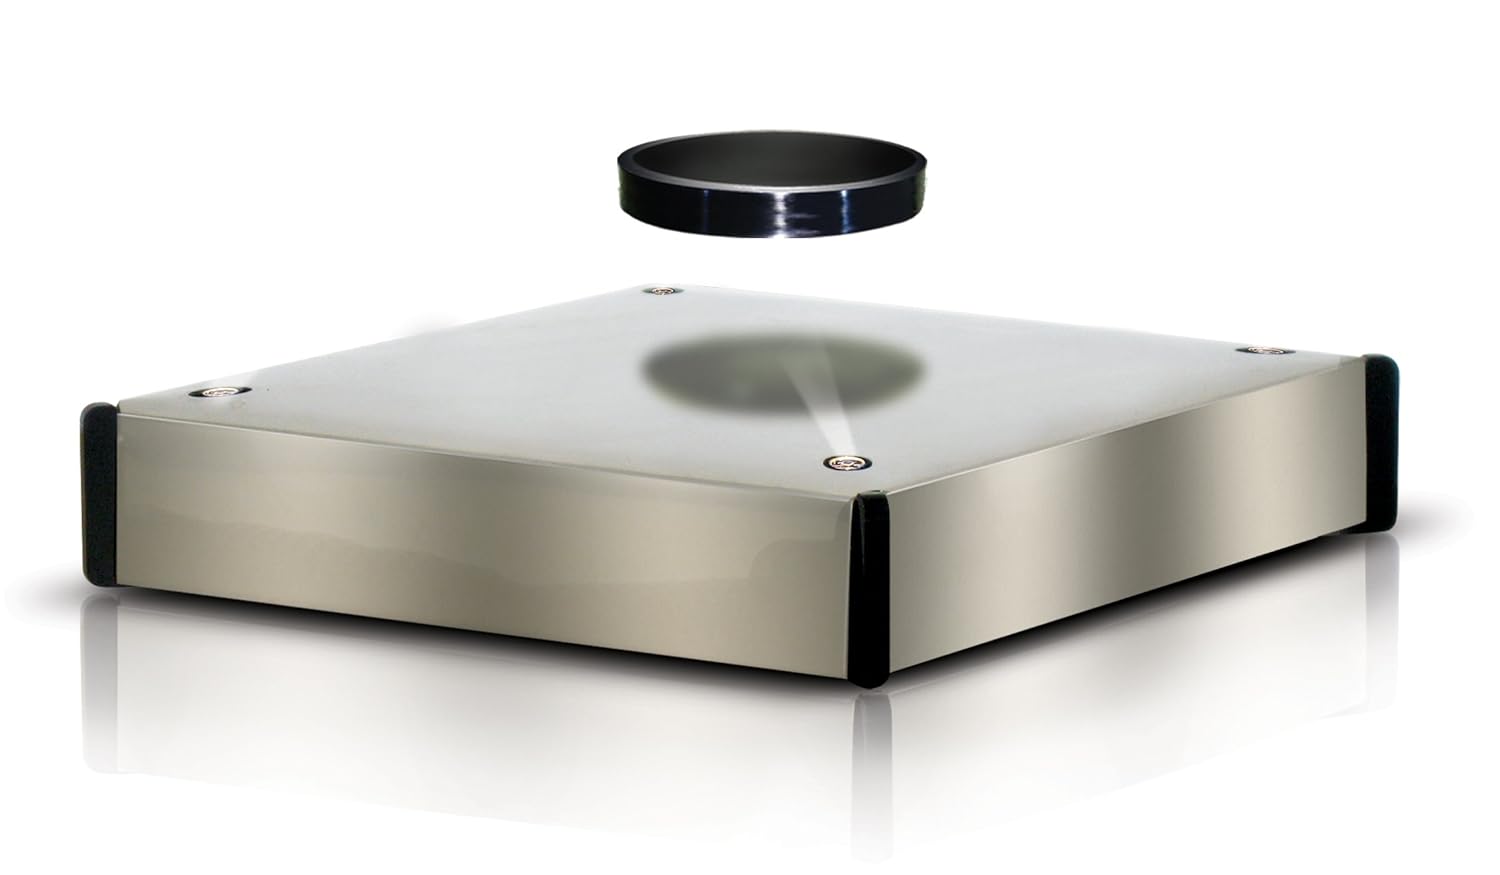
Fascinations Levitron Revolution Platform With EZ Float Technology


  • The Levitron Revolution features EZ Float technology to make levitating your favorite collectibles a snap
  • The levitating magnetic hover disc can hold up to 13 ounces in mid-air
  • 4 white accent LEDs spotlights your item beautifully
  • People wont believe that its possible until they see it for themselves
  • Objects continuously revolve in space inspiring wonder and amazement

 U can buy at: http://goo.gl/GPYkGp

Product Description

From the Manufacturer

Our most advanced levitation device yet.

Product Description

Fascinations Levitron Revolution Platform w/ EZ Float Technology 
Discover the secrets of levitation with Fascinations Levitron Revolution Platform w/ EZ Float Technology. This levitating magic kit comes with a magnetic hover disc that can hold up to 13 oz in midair. Levitron is an attention grabber in all parties as it can levitate models, jewelry, memorabilia and other collectibles.

Why You'll Love It: While the white accent LEDs spotlight the levitated item, the levitron automatically compensates for changes in weight by making up to 1000 corrections per second to the electromagnets contained in the base.

Age: 5 years and up

Features
  • Can hold up to 13 oz in mid air
  • Platform adjusts automatically to changing weights
  • Spotlights to enhance levitating objects
Includes
  • 120V AC wall adapter
  • Instruction manual

Source:www.amazon.com

Sunday, 11 September 2011

Web 4.0 the future of Internet landscape


Further convergence of the online and physical world has led to the emergence of "Web 4.0" - the next generation of internet. Semantic analyzing programs, having evolved into forms of AI, now perform a huge range of automated tasks for business, government and consumers. Running on massively parallel networks, these applications hunt for textual and visual data - combining the most subtle capabilities of humans (such as pattern recognition) with ways in which machines are already vastly superior (such as speed and memory).


In addition to serving as highly advanced search engines, they are playing a major function in the real world - gathering information from the array of sensors, cameras and other tracking devices now present in the environment, on vehicles, and even on people themselves.
Although privacy and civil liberties issues are being raised, this new generation of IT promises to bring enormous benefits to society. Crimes are faster and easier to solve thanks to these intelligent virtual agents; transport and logistics are smoother and more efficient; resources can be managed and distributed more accurately.


In addition, practically every physical document in existence has now been digitally encoded, backed up and archived online. This includes full copies of all books, journals, manuscripts and other literature ever published – forming a complete repository of human knowledge going back thousands of years. These documents can be retrieved and analysed using real-time speech commands, translated from any of the world's 6,000 languages and accessed via 3D holographic imaging.


Web 4.0 is also democratising the Internet more than ever before. News agencies are finding themselves increasingly outmoded by bloggers and other social media when it comes to speed and accuracy of information.


Friday, 19 August 2011

Cross Site Scripting - XSS - Mechanism


Cross Site Scripting - XSS - Mechanism


1. What is Cross Site Scripting?
Cross Site Scripting (or XSS) is one of the most common application-layer web attacks. XSS commonly targets scripts embedded in a page which are executed on the client-side (in the user’s web browser) rather than on the server-side. XSS in itself is a threat which is brought about by the internet security weaknesses of client-side scripting languages, with HTML and JavaScript (others being VBScript, ActiveX, HTML, or Flash) as the prime culprits for this exploit. The concept of XSS is to manipulate client-side scripts of a web application to execute in the manner desired by the malicious user. Such a manipulation can embed a script in a page which can be executed every time the page is loaded, or whenever an associated event is performed.
In a typical XSS attack the hacker infects a legitimate web page with his malicious client-side script. When a user visits this web page the script is downloaded to his browser and executed. There are many slight variations to this theme, however all XSS attacks follow this pattern, which is depicted in the diagram below.

High Level View of an XSS Attack
A basic example of XSS is when a malicious user injects a script in a legitimate shopping site URL which in turn redirects a user to a fake but identical page. The malicious page would run a script to capture the cookie of the user browsing the shopping site, and that cookie gets sent to the malicious user who can now hijack the legitimate user’s session. Although no real hack has been performed against the shopping site, XSS has still exploited a scripting weakness in the page to snare a user and take command of his session. A trick which often is used to make malicious URLs less obvious is to have the XSS part of the URL encoded in HEX (or other encoding methods). This will look harmless to the user who recognizes the URL he is familiar with, and simply disregards and following ‘tricked’ code which would be encoded and therefore inconspicuous.
2. Site owners are always confident, but so are hackers!
Without going into complicated technical details, one must be aware of the various cases which have shown that XSS can have serious consequences when exploited on a vulnerable web application. Many site owners dismiss XSS on the grounds that it cannot be used to steal sensitive data from a back-end database. This is a common mistake because the consequences of XSS against a web application and its customers have been proven to be very serious, both in terms of application functionality and business operation. An online business project cannot afford to lose the trust of its present and future customers simply because nobody has ever stepped forward to prove that their site is really vulnerable to XSS exploits. Ironically, there are stories of site owners who have boldly claimed that XSS is not really a high-risk exploit. This has often resulted in a public challenge which hackers are always itching to accept, with the site owner having to later deal with a defaced application and public embarrassment.
3. The repercussions of XSS
Analysis of different cases which detail XSS exploits teaches us how the constantly changing web technology is nowhere close to making applications more secure. A thorough web search will reveal many stories of large-scale corporation web sites being hacked through XSS exploits, and the reports of such cases always show the same recurring consequences as being of the severe kind.
Exploited XSS is commonly used to achieve the following malicious results:

  • Identity theft
  • Accessing sensitive or restricted information
  • Gaining free access to otherwise paid for content
  • Spying on user’s web browsing habits
  • Altering browser functionality
  • Public defamation of an individual or corporation
  • Web application defacement
  • Denial of Service attacks
Any site owner with a healthy level of integrity would agree that none of the above can really be considered us frivolous or unimportant impacts on a vulnerable site. Security flaws in high-profile web sites have allowed hackers to obtain credit card details and user information which allowed them to perform transactions in their name. Legitimate users have been frequently tricked into clicking a link which redirects them to a malicious but legitimate-looking page which in turn captures all their details and sends them straight to the hacker. This example might not sound as bad as hacking into a corporate database; however it takes no effort to cause site visitors or customers to lose their trust in the application’s security which in turn can result in liability and loss of business.
4. XSS Attack Vectors
Internet applications today are not static HTML pages. They are dynamic and filled with ever changing content. Modern web pages pull data from many different sources. This data is amalgamated with your own web page and can contain simple text, or images, and can also contain HTML tags


DISLAIMER: For education purpose only


Adithya

Caller ID Spoofing


Caller ID Spoofing


Go to this website

http://www.crazycall.net

Fill the asked information i.e.

First select the country
Now insert the mobile number u wanna display
& now insert the victim's mobile number
Press "Get me a code" and we will provide you with number to call and a code.
Call the number
Enter the code and we will connect your call to your friend with the CallerID and voice you have selected.

DISLAIMER: For education purpose only


Adithya 

Share

Twitter Delicious Facebook Digg Stumbleupon Favorites